Real-profile browsing is the kind of agent feature that sounds small until you try to do anything useful on the modern web.
Nous Research shipped it for Hermes Agent on August 27, 2026. Turn it on and the agent no longer starts every session as a stranger with an empty cookie jar. It can act with your logins, from a managed copy of the Chrome-family profile you already use.
That is the difference between “open a public page and summarize it” and “check the dashboard you actually live in, draft the reply in the tool you already use, and submit the form that only exists behind your session.”
Hermes already had real browser control. It can navigate, click, type, snapshot pages as accessibility trees, and run against local Chromium or cloud backends such as Browser Use, Browserbase, and Firecrawl.
The default local session was still a clean, throwaway profile. The agent was logged into nothing.
That is fine for public research. It is a dead end for the work people actually want an agent to do:
Workarounds existed. You could attach Hermes to a running Chrome via CDP and /browser connect, keep a dedicated --user-data-dir, or hand the agent a session through an extension. All of those work. None of them is “flip a setting and keep using the browser you already have.”
Real-profile browsing is that flip.
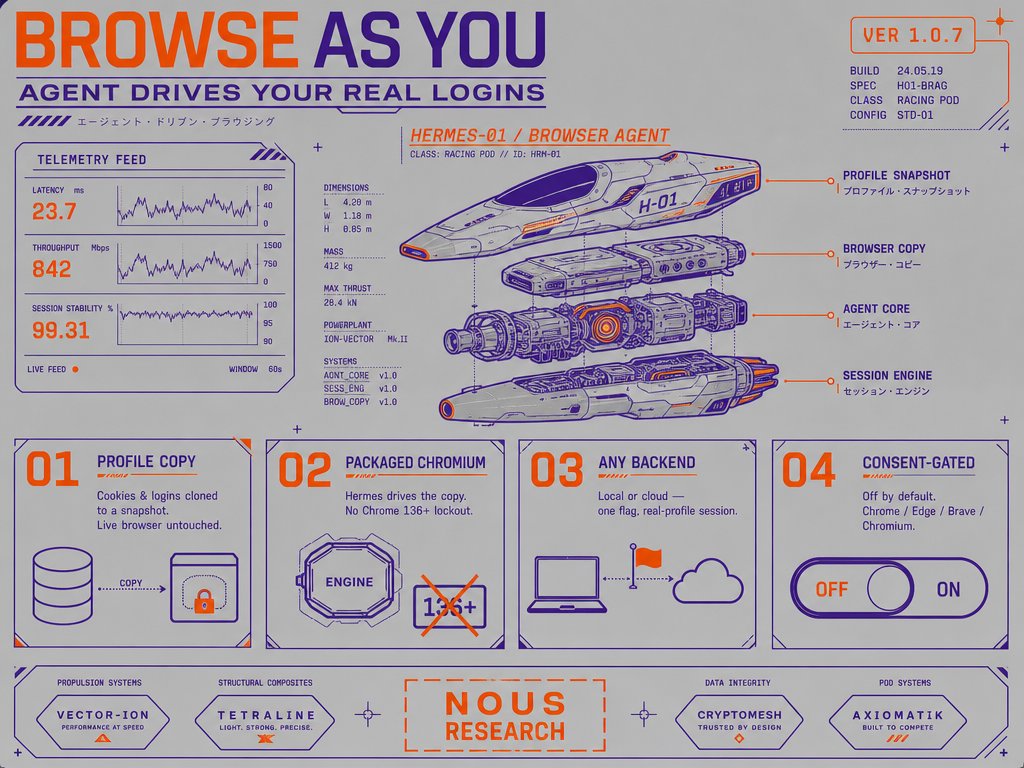
Hermes does not remote-debug your live profile. That is the important design choice.
When the feature is on, it:
Local State → profile.last_used so it copies only the profile you actually browse.~/.hermes/browser-profile/<browser>/.Your running browser is left alone. The snapshot is a separate directory, so Hermes does not fight the profile lock, and it sidesteps Chrome 136+ blocking remote debugging on the default user-data directory.
Auth files re-sync from your real profile whenever a fresh agent session starts. Log in to a site in your own browser, start a new Hermes browser session, and the agent should see that login. Other Chrome profiles are never copied.
Turn the feature off and Hermes deletes ~/.hermes/browser-profile/ on the next browser use. The copied credentials are not supposed to linger after you revoke consent.
In config:
# ~/.hermes/config.yaml
browser:
  use_real_profile: true
In Hermes Desktop: Settings → Browser → Use My Real Browser Profile.
It is off by default. That is not an accident.
On a local backend, the snapshot is used automatically once the toggle is on.
If you are on a cloud browser backend, cloud sessions stay isolated. The agent can still open a real-profile local session on demand through the browser_exec tool’s local argument. That argument only appears when the toggle is enabled. Cloud work keeps running as cloud work. Authenticated-as-you work can stay on the machine that holds your profile.
That hybrid path matters. Stealth, proxies, and CAPTCHA-solving still belong in the cloud. Your bank tab, company SSO, and personal Gmail do not.
On macOS and Linux, Hermes can copy the profile while the browser is running.
On Windows, Chrome, Edge, and Brave hold cookie and login databases with an exclusive lock. If the browser is open — including a tray or “continue running background apps” process — the copy fails fast with a “fully quit the browser and retry” message instead of hanging or handing the agent a signed-out session.
There is an optional helper:
browser:
  real_profile_autoclose: true
This does not silently kill Chrome. If the profile is locked, Hermes stops and asks. Only after you approve does it run hermes browser close-profile, which terminates that profile’s process tree and drops unsaved tabs. If a background instance comes back, Hermes will not loop and kill again on its own.
Firefox as the OS default fails closed. Hermes will not guess at a non-Chromium profile.
Nous’s own framing is the right one: consent-gated convenience, not isolation.
A page the agent visits runs with your real logins. If the agent clicks the wrong thing, the action happens as you. If the snapshot leaks, the cookies and saved logins leak with it. Community reaction landed in the same place: the capability is huge, and handing an agent your saved logins is a trust fall.
Practical rules of thumb:
~/.hermes/browser-profile/ as credential storage.If you only need a public page, leave it off. A clean profile is the safer default.
Browser automation for agents has been converging on the same stack for months: real Chromium, accessibility-tree snapshots, tool calls or a Browser Use script, cloud or local backends. Hermes was already in that world.
Identity was the missing piece.
The interesting web is not the open web. It is the web behind the cookies you already earned. An agent that can read trending GitHub is useful. An agent that can operate the same logged-in tools you use all day is a different product.
Real-profile browsing does not invent that idea. It makes the idea local, explicit, and reversible: a snapshot, a toggle, a delete-on-revoke path, and a warning that this is you, not a sandbox.
That is the right shape for a dangerous feature. Off until you ask. Copied, not attached. Re-synced, not permanently forked. Deleted when you change your mind.
Use it when you want Hermes in your session. Leave it off when you do not. The feature is only as good as that habit.